
PCI DSS Compliance for MSPs
Turn PCI DSS v4.0 Prep into a Recurring MSP Service
Any client that takes card payments needs PCI DSS. Nuronus gives your MSP the platform to scope the environment, map all 12 PCI DSS v4.0 requirements, collect evidence, and deliver audit-ready readiness reports — as a high-margin service.
Free for 2 clients. All features included. No credit card required.
How It Works
PCI Readiness in Four Phases
01
Scope the CDE
Define the cardholder data environment and select the correct SAQ. Nuronus guides scoping based on how the client handles card data.
02
Assess Current Controls
Run an automated assessment against all 12 PCI DSS v4.0 requirements. Identify gaps and generate a remediation roadmap.
03
Collect Evidence & Policies
Use automated evidence collection and the AI policy generator to build the complete PCI documentation package.
04
Deliver & Monitor
Hand off audit-ready documentation. Set up continuous monitoring to maintain compliance between assessment periods.
Capabilities
What you can bill for on PCI DSS
Nuronus handles the heavy lifting of PCI DSS preparation so you can focus on delivering value to your clients and growing your compliance practice.
Scoping & SAQ Guidance
Nuronus helps you determine each client's cardholder data environment and the right Self-Assessment Questionnaire, so the engagement is scoped correctly from day one.
Sell PCI scoping as a fixed-fee first engagement
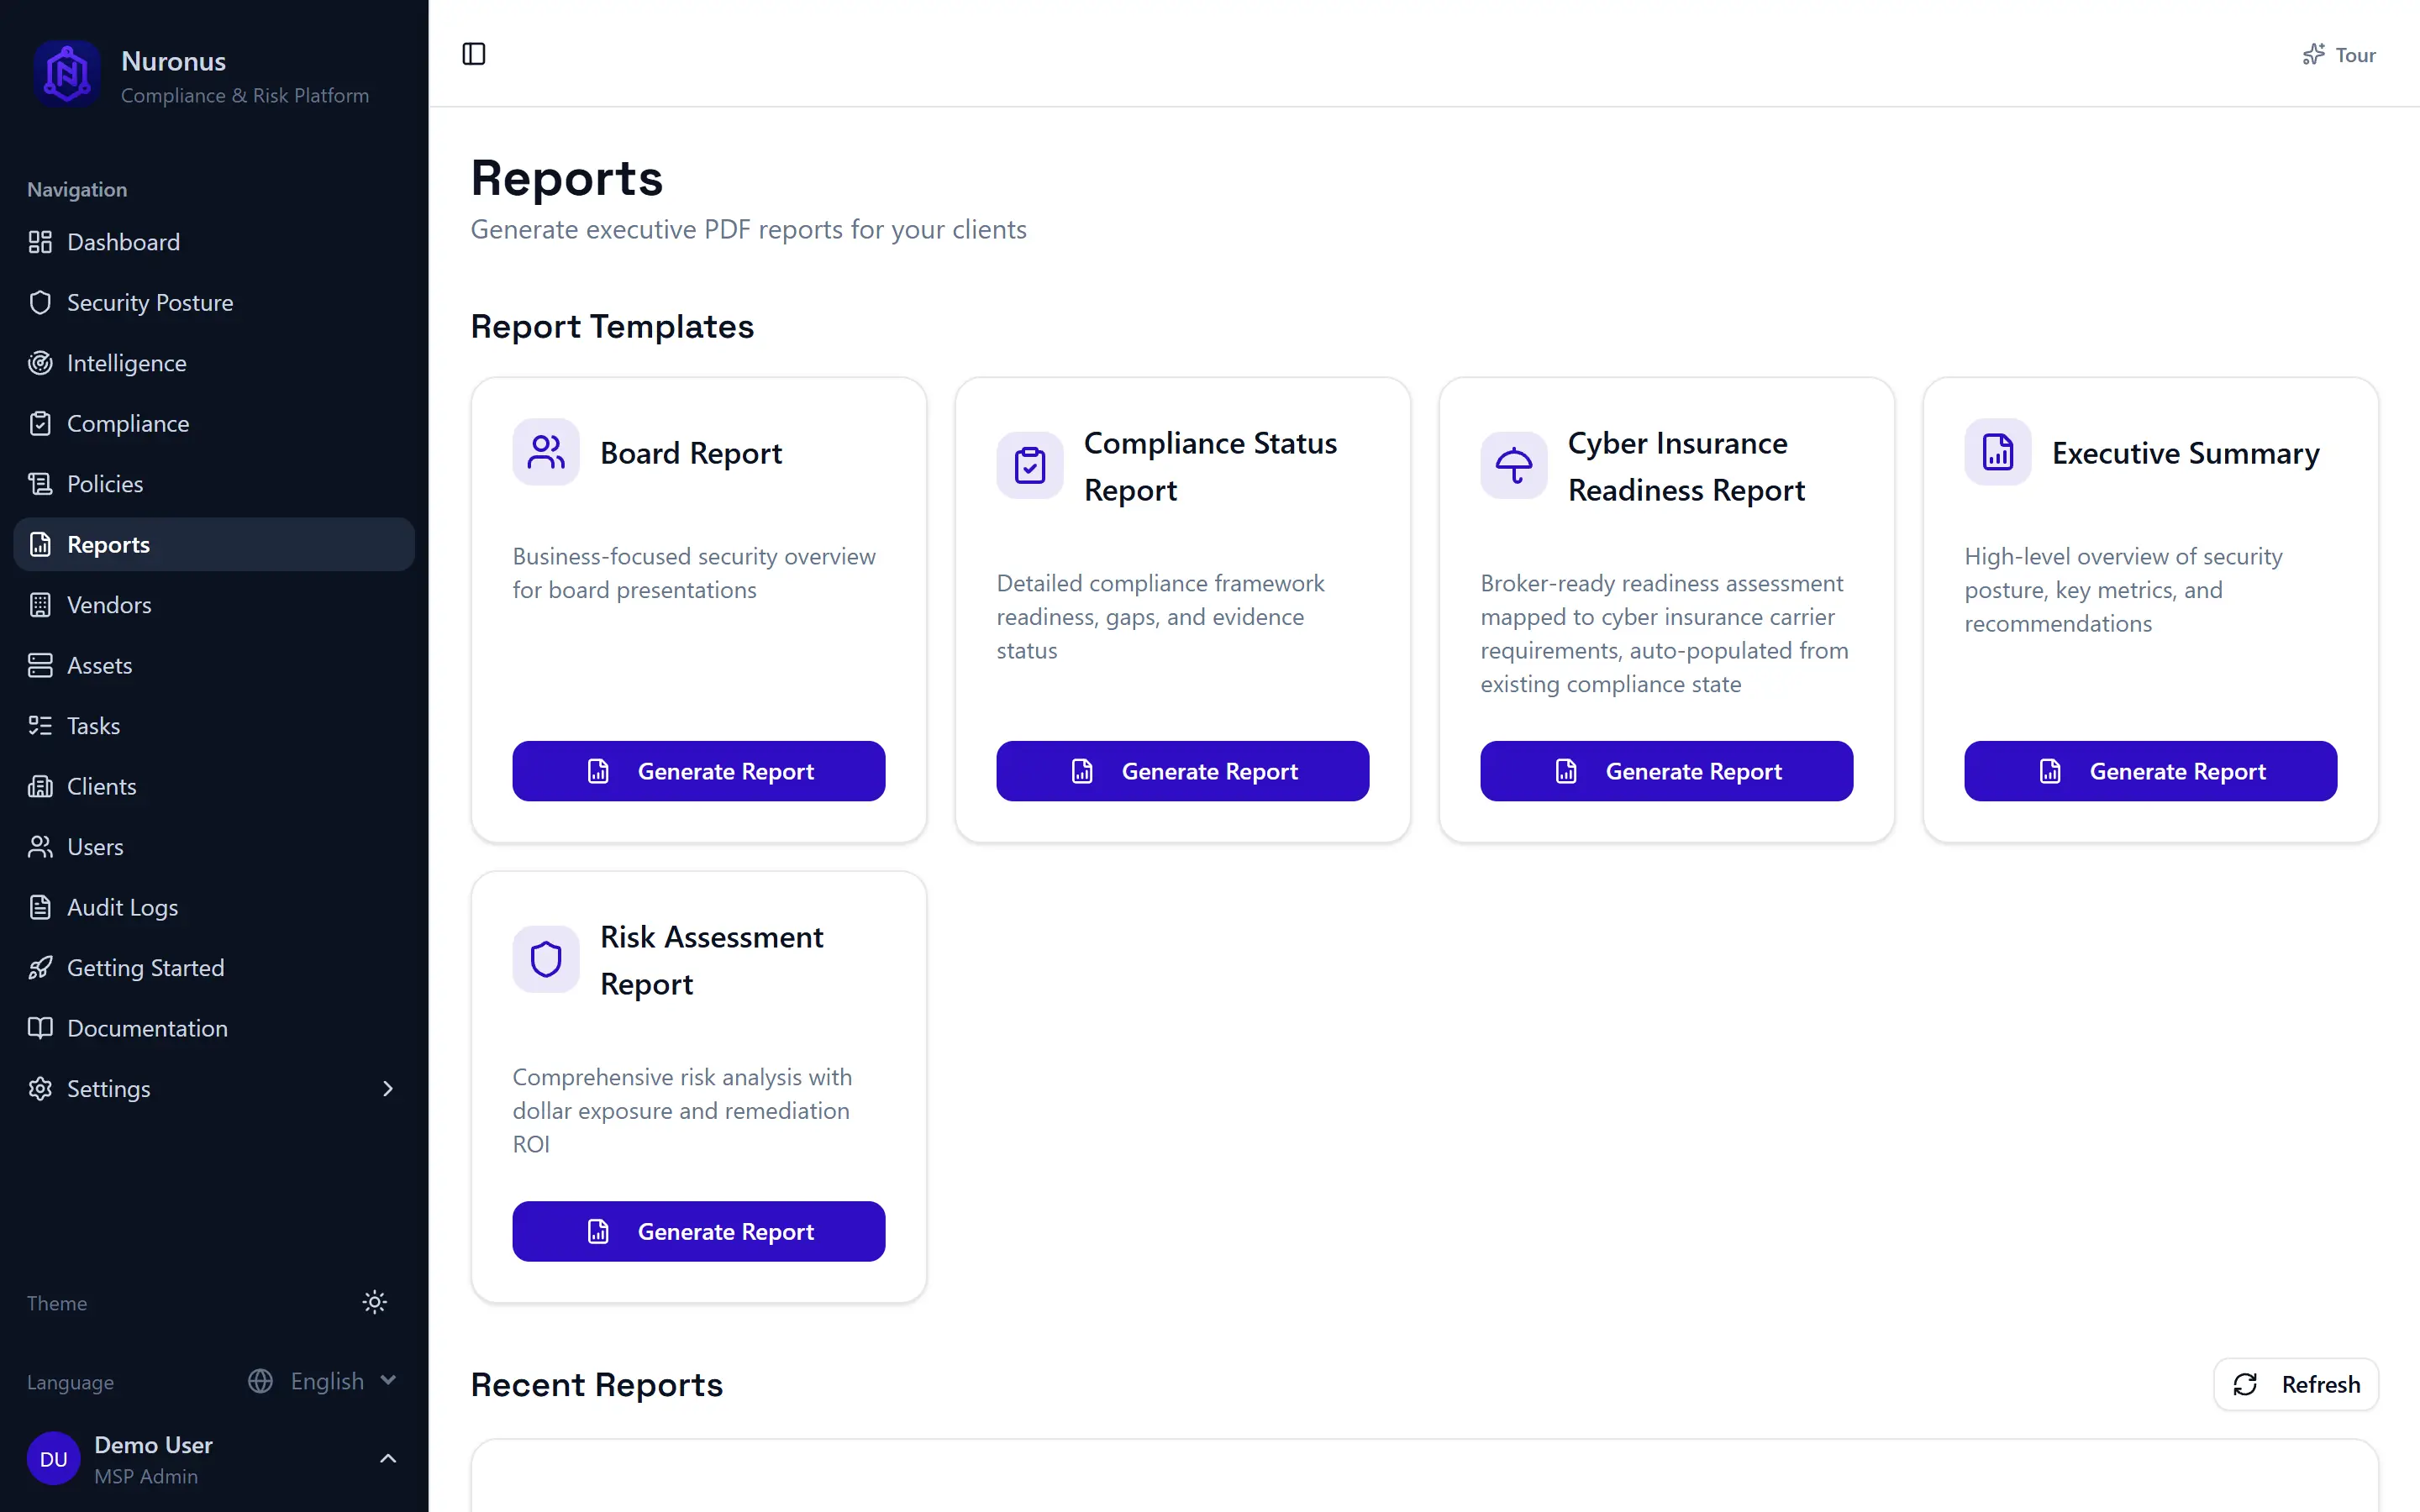
PCI DSS v4.0 Control Mapping
All 12 PCI DSS v4.0 requirements mapped to one underlying control set. See exactly which controls are met, partially met, or missing for each client.
One assessment, reused across every framework a client needs
Evidence Collection & Organization
A centralized evidence repository linked to specific PCI requirements. Pull evidence from connected environments instead of hunting through email threads.
Cut evidence collection time dramatically
Remediation & Readiness Reporting
Track remediation across all 12 requirements, assign owners and deadlines, and hand clients an audit-ready, white-label PCI readiness report.
Provide ongoing PCI monitoring as a monthly service
The Problem
Every Client Taking Card Payments Needs PCI. Few MSPs Offer It.
PCI DSS applies to any business that stores, processes, or transmits cardholder data — retail, hospitality, healthcare, professional services. Your clients need help getting compliant, but traditional PCI consulting is expensive and slow. MSPs who can deliver PCI readiness own a recurring, high-margin revenue stream.
- Clients that take card payments need PCI DSS — but have no idea where to start
- PCI DSS v4.0 added new requirements, and the old spreadsheet approach no longer holds up
- Determining the right SAQ (A, A-EP, D…) and scope is confusing and error-prone
- Evidence is scattered across email, portals, and screenshots at renewal time
- QSA and consulting engagements are priced out of reach for most SMB clients
The Standard
All 12 PCI DSS v4.0 Requirements, Covered
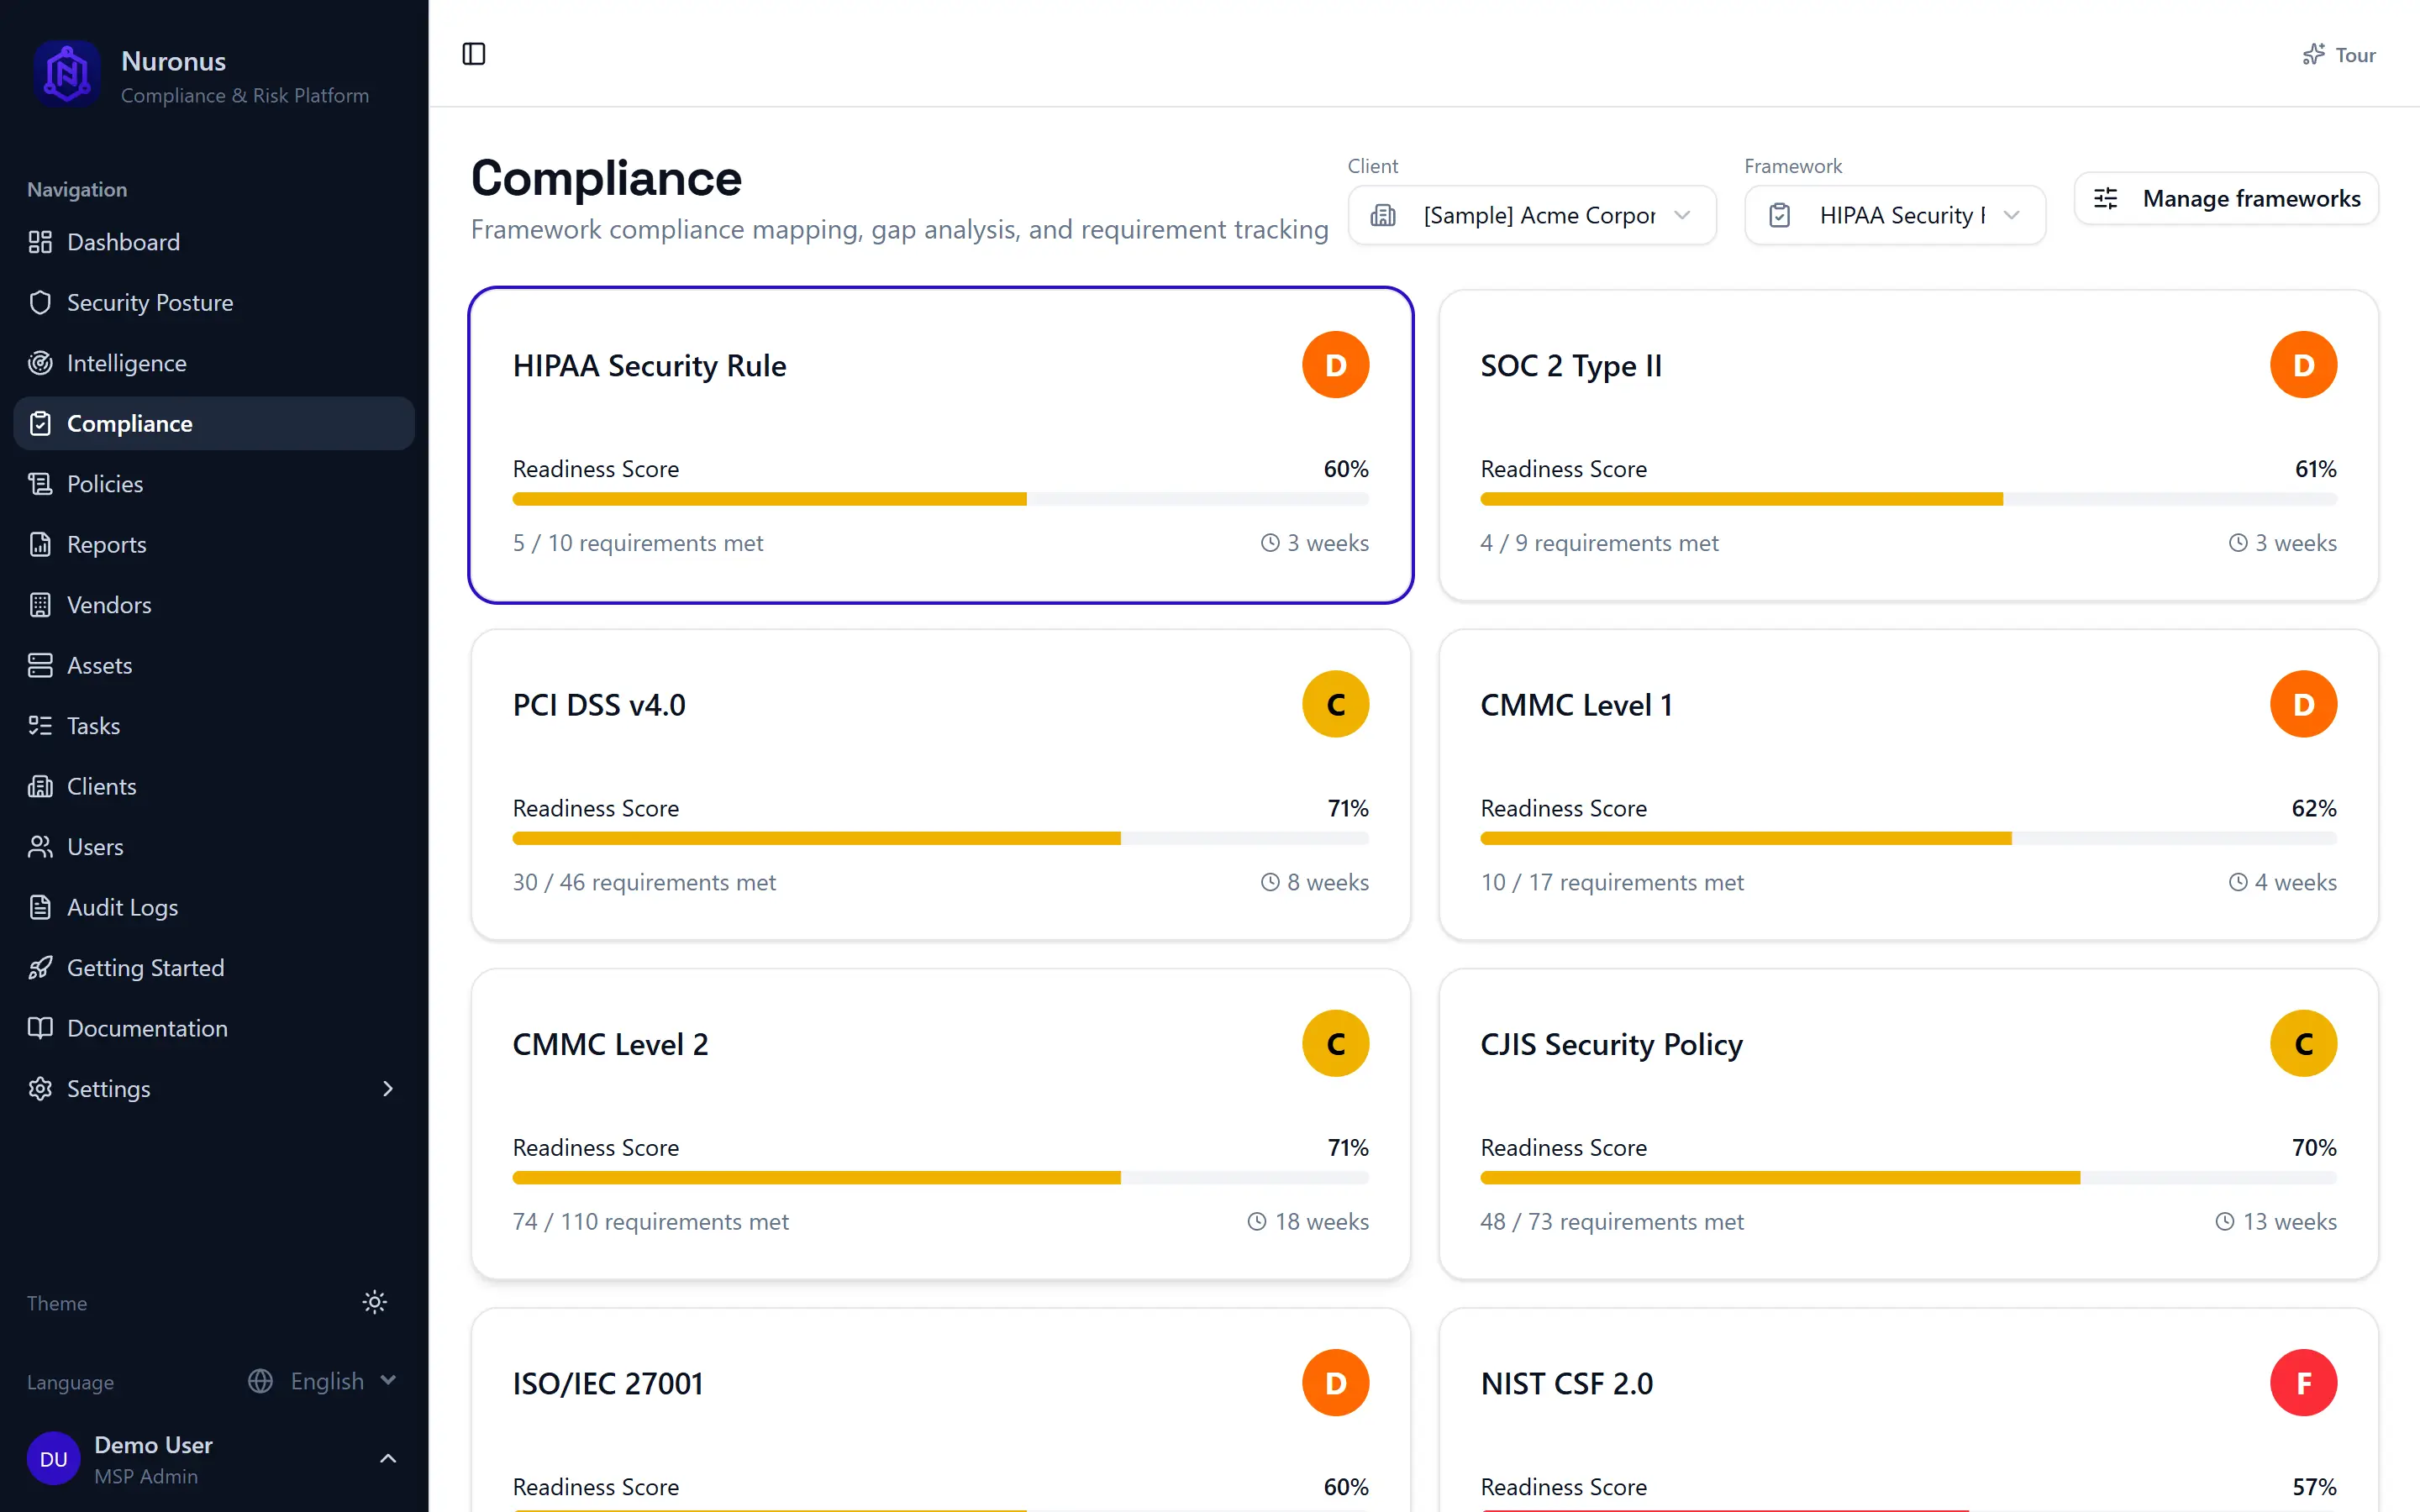
Nuronus maps every PCI DSS v4.0 requirement to a single control set, so a client's one assessment feeds PCI and every other framework they fall under.
Build & Maintain a Secure Network
- 1. Install and maintain network security controls
- 2. Apply secure configurations to all system components
Protect Account Data
- 3. Protect stored account data
- 4. Protect cardholder data with strong cryptography in transit
Maintain a Vulnerability Management Program
- 5. Protect all systems and networks from malicious software
- 6. Develop and maintain secure systems and software
Implement Strong Access Control
- 7. Restrict access to system components and cardholder data
- 8. Identify users and authenticate access
- 9. Restrict physical access to cardholder data
Regularly Monitor & Test Networks
- 10. Log and monitor all access to cardholder data
- 11. Test security of systems and networks regularly
Maintain an Information Security Policy
- 12. Support information security with organizational policies
FAQ
PCI Compliance for MSPs, Answered
Can an MSP deliver PCI DSS compliance as a service?
Yes. MSPs are well positioned to deliver PCI DSS readiness — scoping the cardholder data environment, mapping controls, collecting evidence, and producing a readiness report. Nuronus gives you the platform to do this repeatably across clients and charge for it as a managed service. Formal validation for larger merchants still involves a QSA, but most SMB clients self-assess via an SAQ.
What is the difference between PCI DSS v3.2.1 and v4.0?
PCI DSS v4.0 is the current standard and adds requirements around authentication, targeted risk analysis, and continuous security rather than point-in-time checks. Nuronus maps to PCI DSS v4.0 so your clients are assessed against the current requirements.
Which PCI SAQ does my client need?
It depends on how the client accepts and processes card payments — SAQ A for fully outsourced e-commerce, A-EP for partially outsourced, D for merchants storing cardholder data, and so on. Nuronus helps you scope the environment and identify the applicable SAQ before you start.
How much does PCI compliance software cost for MSPs?
Nuronus is free for up to 2 clients with the full platform, then flat per-client pricing from $149/month — no per-endpoint fees. That lets you price PCI readiness engagements with a predictable, markable cost base.
Does Nuronus support other frameworks besides PCI DSS?
Yes — eleven frameworks in total: HIPAA, SOC 2, PCI DSS, NIST CSF, ISO 27001, CIS Controls v8, CJIS, CMMC, FERPA, PIPEDA, and Loi 25 (Quebec Law 25). All map to one underlying control set, so a single assessment covers every framework a client falls under.
Add PCI Services to Your MSP This Week
Free forever for 2 clients. All features included. No credit card, no sales call. Sign up and explore with pre-loaded demo data.
Pre-loaded with demo data. Explore before you connect a live client.