
CIS Controls for MSPs
Sell CIS Controls v8 IG1 as a Recurring Security Baseline
CIS Controls v8 Implementation Group 1 is essential cyber hygiene — 56 Safeguards across 18 Controls. Nuronus uses CIS IG1 as its master control set, so one scored assessment feeds every other framework your clients need, with white-label reports you can bill monthly.
Free for 2 clients. All features included. No credit card required.
How It Works
How MSPs productize CIS IG1
01
Scope the Baseline
Pick the client and confirm CIS Controls v8 IG1 as the starting baseline. Nuronus already treats IG1 as the master control set behind every mapped framework.
02
Assess Against IG1
Walk the Safeguards, mark status from live checks, and generate a scored gap list your technicians can close in priority order.
03
Attach Evidence
Link RMM exports, policies, screenshots, and attestations to each control check so the baseline has an audit trail, not just a green checkbox.
04
Report and Expand
Deliver a white-label CIS readiness report, then reuse the same control posture when the client needs HIPAA, SOC 2, NIST CSF, or another mapped framework.
Capabilities
What a CIS IG1 program looks like for an MSP portfolio
Assess each client against the CIS Controls v8 IG1 Safeguards that Nuronus seeds as its master checklist, attach evidence to live control checks, and reuse that same posture when you report against mapped frameworks.
IG1 Assessment & Scoring
Score clients against CIS Controls v8 Implementation Group 1 from a multi-tenant dashboard. See which Safeguards are met, partial, or missing, with a prioritized remediation list your techs can work.
Sell a fixed-fee CIS baseline assessment as the first engagement
Master Control Set for Every Framework
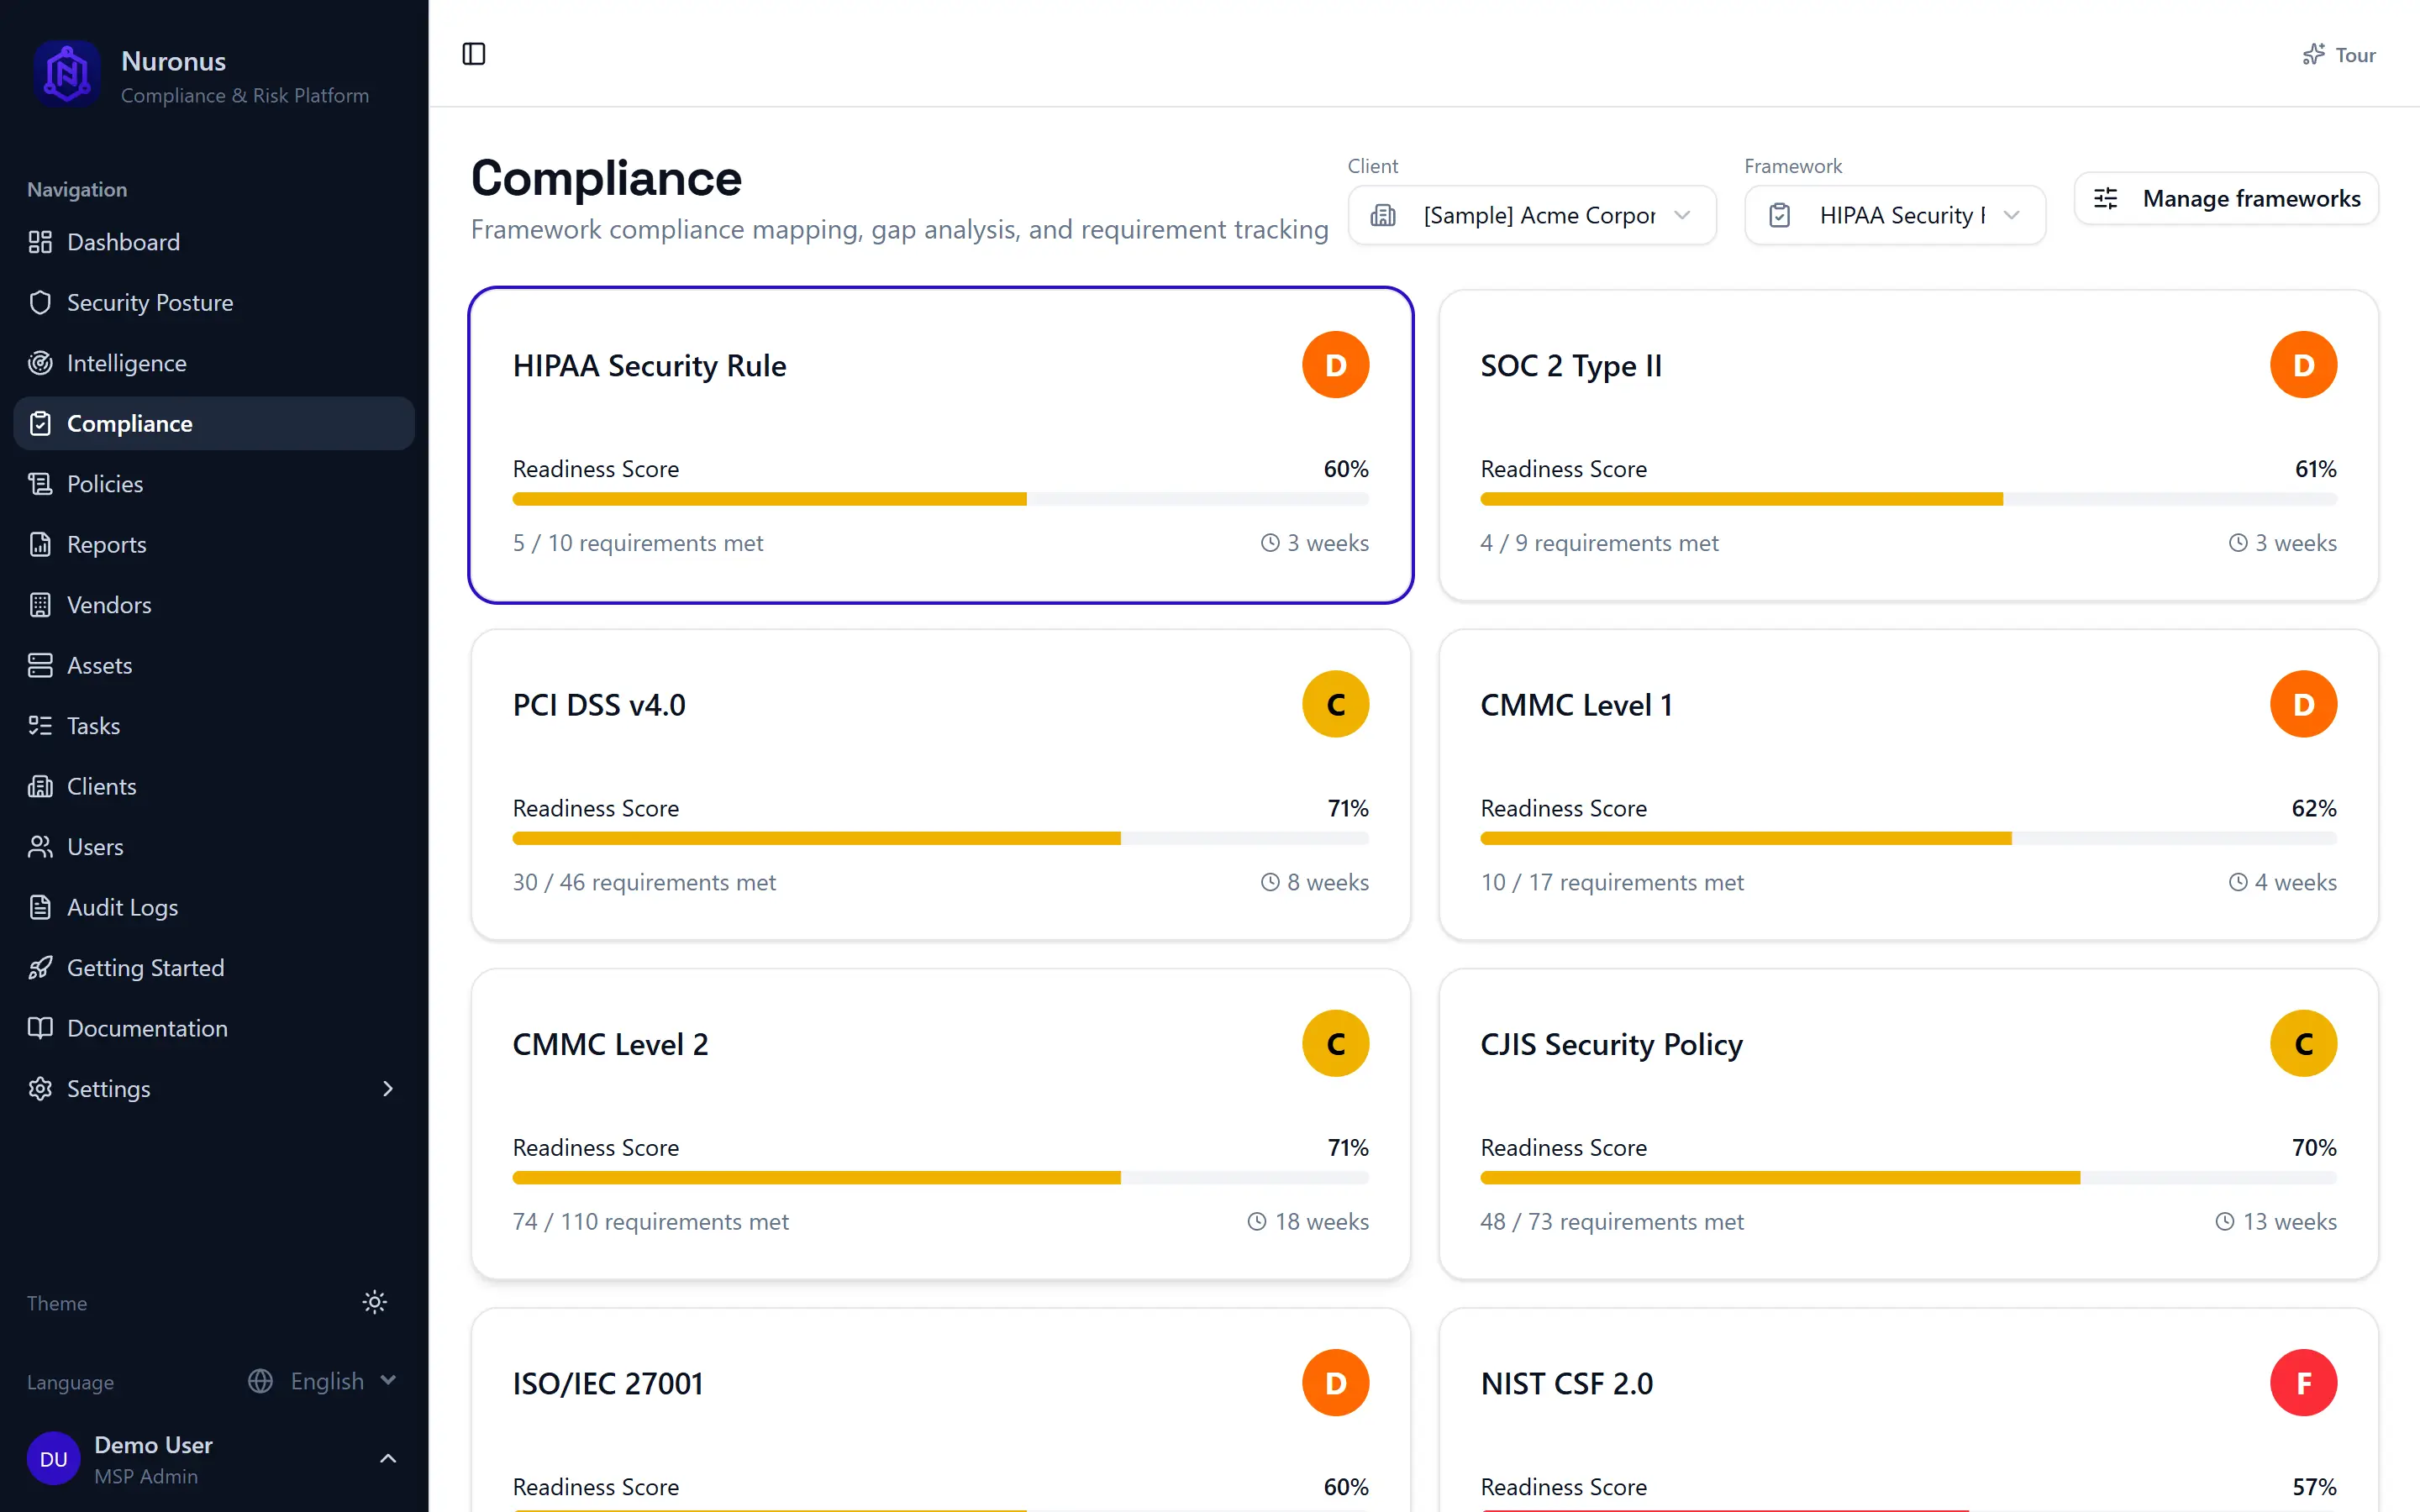
CIS IG1 is the control set Nuronus builds on. HIPAA, SOC 2, PCI DSS, NIST CSF, CMMC, and the rest map onto those same controls — assess once, report against every framework a client falls under.
One assessment, reused across every framework you sell
Evidence Tied to Controls
Attach screenshots, policies, attestations, and exports to specific CIS control checks instead of hunting through ticket threads when a client or insurer asks for proof.
Keep a living evidence pack as a monthly retainer deliverable
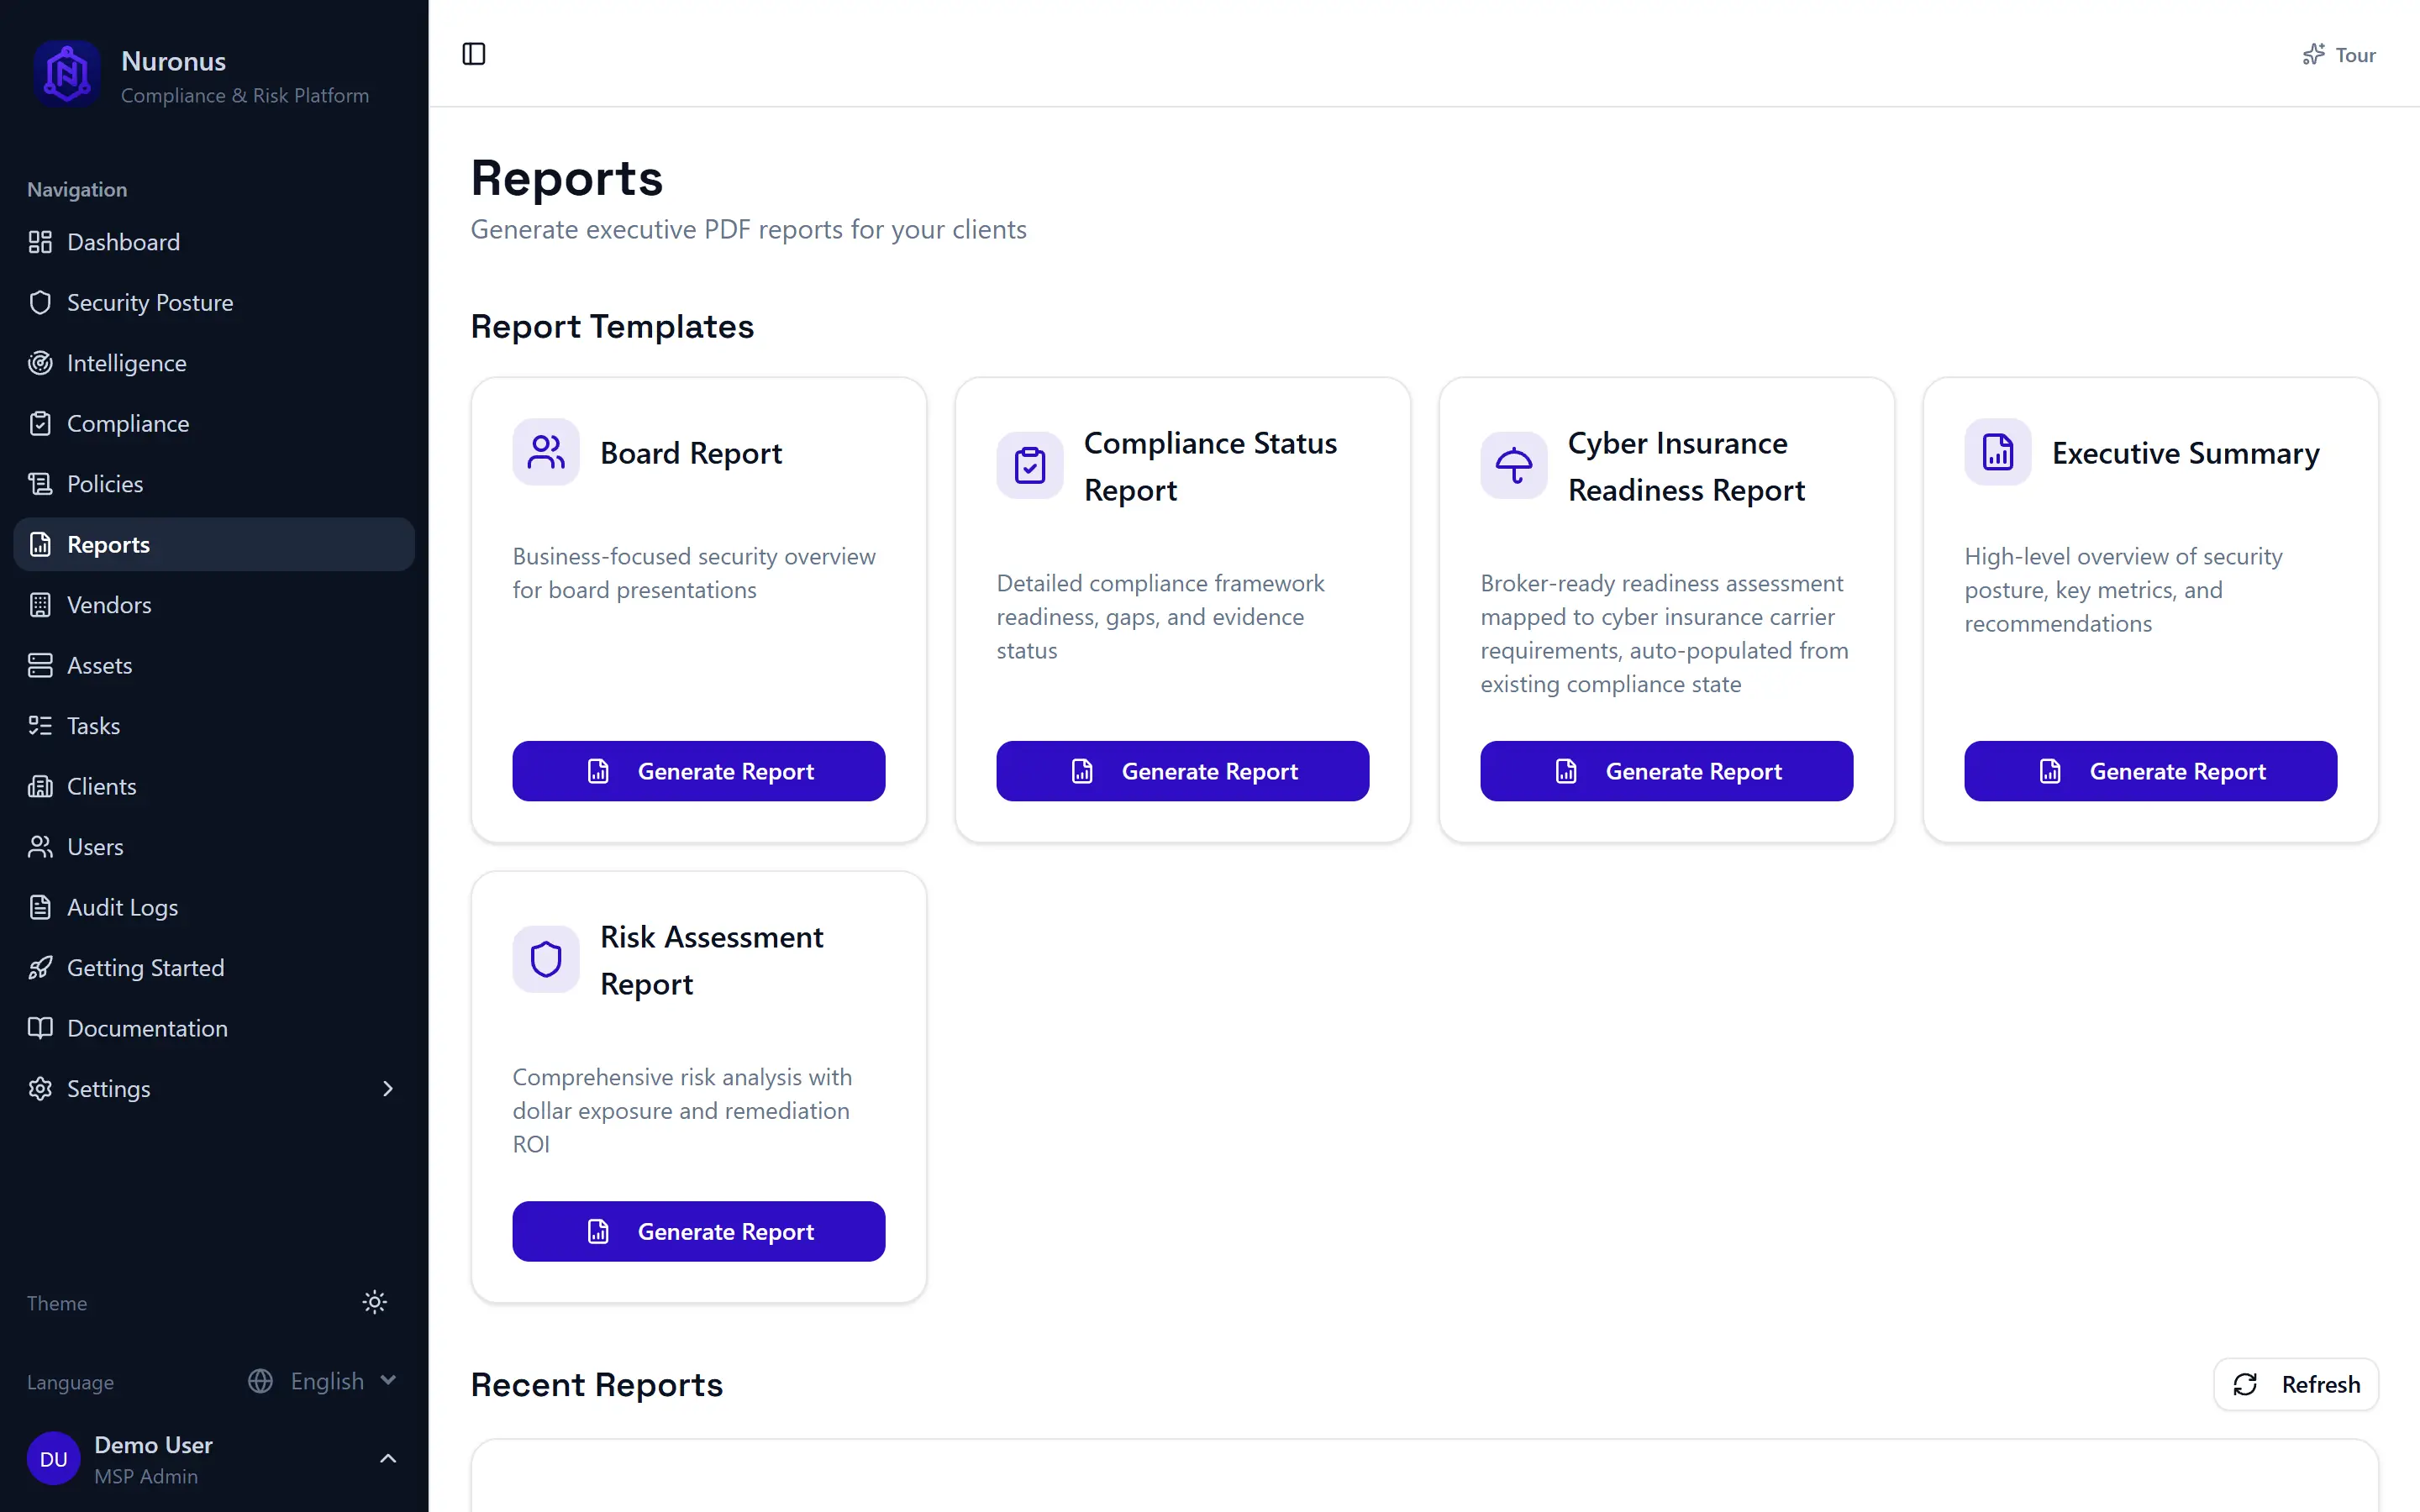
White-Label Baseline Reporting
Hand clients a branded readiness report showing CIS posture, open gaps, and trend over time — from the same dashboard you use for every other framework.
Turn day-to-day MSP work into a leadership-level conversation
The Problem
Clients Want a Security Baseline. Spreadsheets Don't Scale.
CIS Controls v8 IG1 is the practical starting point most SMBs should hit first — asset inventory, MFA, patching, backups, logging, and basic incident handling. MSPs already do much of that work in the RMM. Without a scored control record and evidence trail, none of it becomes a compliance service clients will pay for every month.
- You harden endpoints and patch monthly, but have no scored CIS readiness report to show the client
- Insurers and boards ask for a control baseline; a ticket history is not a defensible answer
- Tracking 56 IG1 Safeguards in a spreadsheet breaks as soon as you have more than a handful of clients
- Evidence lives in the RMM, email, and SharePoint — nowhere tied to a specific control
- When a client later needs HIPAA, SOC 2, or CMMC, you start over instead of reusing the same control set
The Framework
CIS Controls v8 IG1, Grouped for MSP Delivery
CIS Controls v8 organizes 18 Controls; Implementation Group 1 is the essential set of 56 Safeguards for organizations with limited cybersecurity resources. Nuronus tracks IG1 as its master control checklist. Below are the Control families MSPs hit most often when delivering a baseline — described by intent, not as a substitute for the official CIS Safeguard text.
Inventory & Assets (Controls 1–2)
- Detailed enterprise asset inventory and unauthorized asset handling
- Software inventory, supported software only, and unauthorized software removal
Data Protection (Control 3)
- Data management process and data inventory
- Access control lists, retention, and end-user device encryption
Secure Configuration (Control 4)
- Secure configuration process for assets and software
- Default account management on enterprise assets and software
Account & Access Management (Controls 5–6)
- Account inventory, unique passwords, dormant account disablement
- Dedicated admin accounts; access grant and revoke processes
- MFA for externally exposed apps, remote access, and administrative access
Vulnerability & Audit Logging (Controls 7–8)
- Vulnerability management and remediation process
- Automated OS and application patch management
- Audit log process, collection, and adequate storage
Email, Web & Malware (Controls 9–10)
- Supported browsers and email clients; DNS filtering
- Anti-malware deployment, signature updates, and autorun/autoplay disablement
Data Recovery & Network (Controls 11–12)
- Recovery process, automated backups, protected and isolated recovery data, recovery testing
- Network infrastructure kept up to date
Awareness, Providers & Incident Response (Controls 14, 15, 17)
- Security awareness program and social-engineering recognition training
- Service provider inventory
- Incident handling personnel, reporting contacts, and enterprise incident reporting process
FAQ
CIS Controls for MSPs, Answered
What is CIS Controls v8 Implementation Group 1?
CIS Controls v8 is a prioritized set of defensive actions published by the Center for Internet Security. Implementation Group 1 (IG1) is the essential cyber hygiene set — 56 Safeguards across the 18 Controls — aimed at organizations with limited cybersecurity resources. It is a voluntary best-practice baseline, not a certification program.
How does Nuronus use CIS IG1?
CIS Controls v8 IG1 is the master control set Nuronus uses. Other frameworks (HIPAA, SOC 2, PCI DSS, NIST CSF, CMMC, and more) map onto those CIS controls. When you update a control check, notes, or evidence, that shared state feeds every mapped framework view — assess once, report many ways.
Can an MSP sell CIS Controls as a service?
Yes. MSPs already perform much of IG1 through RMM, identity, backup, and ticket work. Nuronus turns that into a scored baseline, evidence pack, and white-label report you can price as a recurring compliance service — then upsell mapped frameworks without redoing the underlying assessment.
Does Nuronus certify clients against CIS Controls?
No. Nuronus helps you assess readiness, track Safeguards, collect evidence, and produce reports. CIS Controls are a voluntary framework; Nuronus does not issue CIS certification, and we do not invent pass rates or guarantee any third-party outcome.
How much does it cost to start?
Nuronus is free for your first 2 clients with all features included and no credit card required. Paid plans start at $149/month as you add clients, so you can prove the CIS baseline service on real engagements before you scale it across the portfolio.
Make CIS IG1 the baseline you bill every month
Assess clients against CIS Controls v8 IG1, attach evidence to live controls, and reuse that posture for every mapped framework. Start with two clients free.
Free for 2 clients. All features included. No credit card required.